This action will delete this post on this instance and on all federated instances, and it cannot be undone. Are you certain you want to delete this post?

INT. REDMOND, BUILDING 34. 3:47 AM. A conference room that smells like cold pizza and regret.
Office 365 EVP: Talk to me. Why is Exchange still down?
MID-LEVEL MANAGER (Dave): So, good news and bad news.
EVP: Give me the good news.
DAVE: We found the service that's failing.
EVP: Great. Who owns it?
DAVE: That's the bad news. It's called auth-bridge-final-v2-REAL. The commit history says it was written by "Copilot" and approved by "Copilot."
EVP: Then get the engineer who prompted it.
DAVE: That was Priya. She was in the Q2 "efficiency realignment."
EVP: Her backup?
DAVE: Also realigned. So was her backup's backup. The whole team is a Slack channel now, and the only one in it is a bot that posts "🚀 LGTM" on every PR.
EVP: Fine. Then we read the code and fix it.
DAVE: We tried. It's 340,000 lines of Python that calls a Rust binary that calls a PowerShell script that curls a Gist. The Gist's README just says "dont touch this lol."
EVP: Documentation?
DAVE: One Confluence page called "Architecture (TODO)." Last edited in 2024. The only content is a Mermaid diagram that fails to render.
EVP: Jesus Christ. Can we roll back?
DAVE: To what? The rollback pipeline was also vibe coded. The last time someone ran it, it rolled back to a version that only existed in the AI's hallucination of what the service should look like.
EVP: So what the fuck have we actually been doing for nine hours?
DAVE: Rebooting servers one at a time and praying. Comms is calling that "restarting affected infrastructure."
EVP: ...Is there anyone left who understands how any of this works?
DAVE: Gary.
EVP: Who's Gary?
DAVE: Contractor. 61 years old. He wrote the original Exchange routing logic in 2003 and he's the only one who knows why there's a sleep(7) in the auth handshake. We let him go in January, but HR forgot to disable his VPN.
EVP: Call Gary.
DAVE: Gary says his rate is now $900 an hour, with a 40-hour minimum, and he wants it in writing that he was right about everything.
EVP: ...Pay Gary.
DAVE: Also, the board wants to know if this will affect the AI efficiency numbers for the earnings call.
EVP: Tell them the outage was caused by "an unexpected interaction during a routine change," and that AI agents are "actively assisting with remediation."
DAVE: Are they?
EVP: Copilot opened a ticket.
DAVE: What did the ticket say?
EVP: "Have you tried turning it off and on again?"
30 years of Internet transfers with curl
https://daniel.haxx.se/blog/2026/11/11/30-years-of-internet-transfers-with-curl/

eMudhra's incident report is out! A Python script truncated their CA private keys to one byte?!
Perhaps we all misunderstood Jensen Huang when he said that we should be embracing agents in this age of AI.

LOL wie kreativ doch Menschen sind. Wie cool. https://checksum24.de/
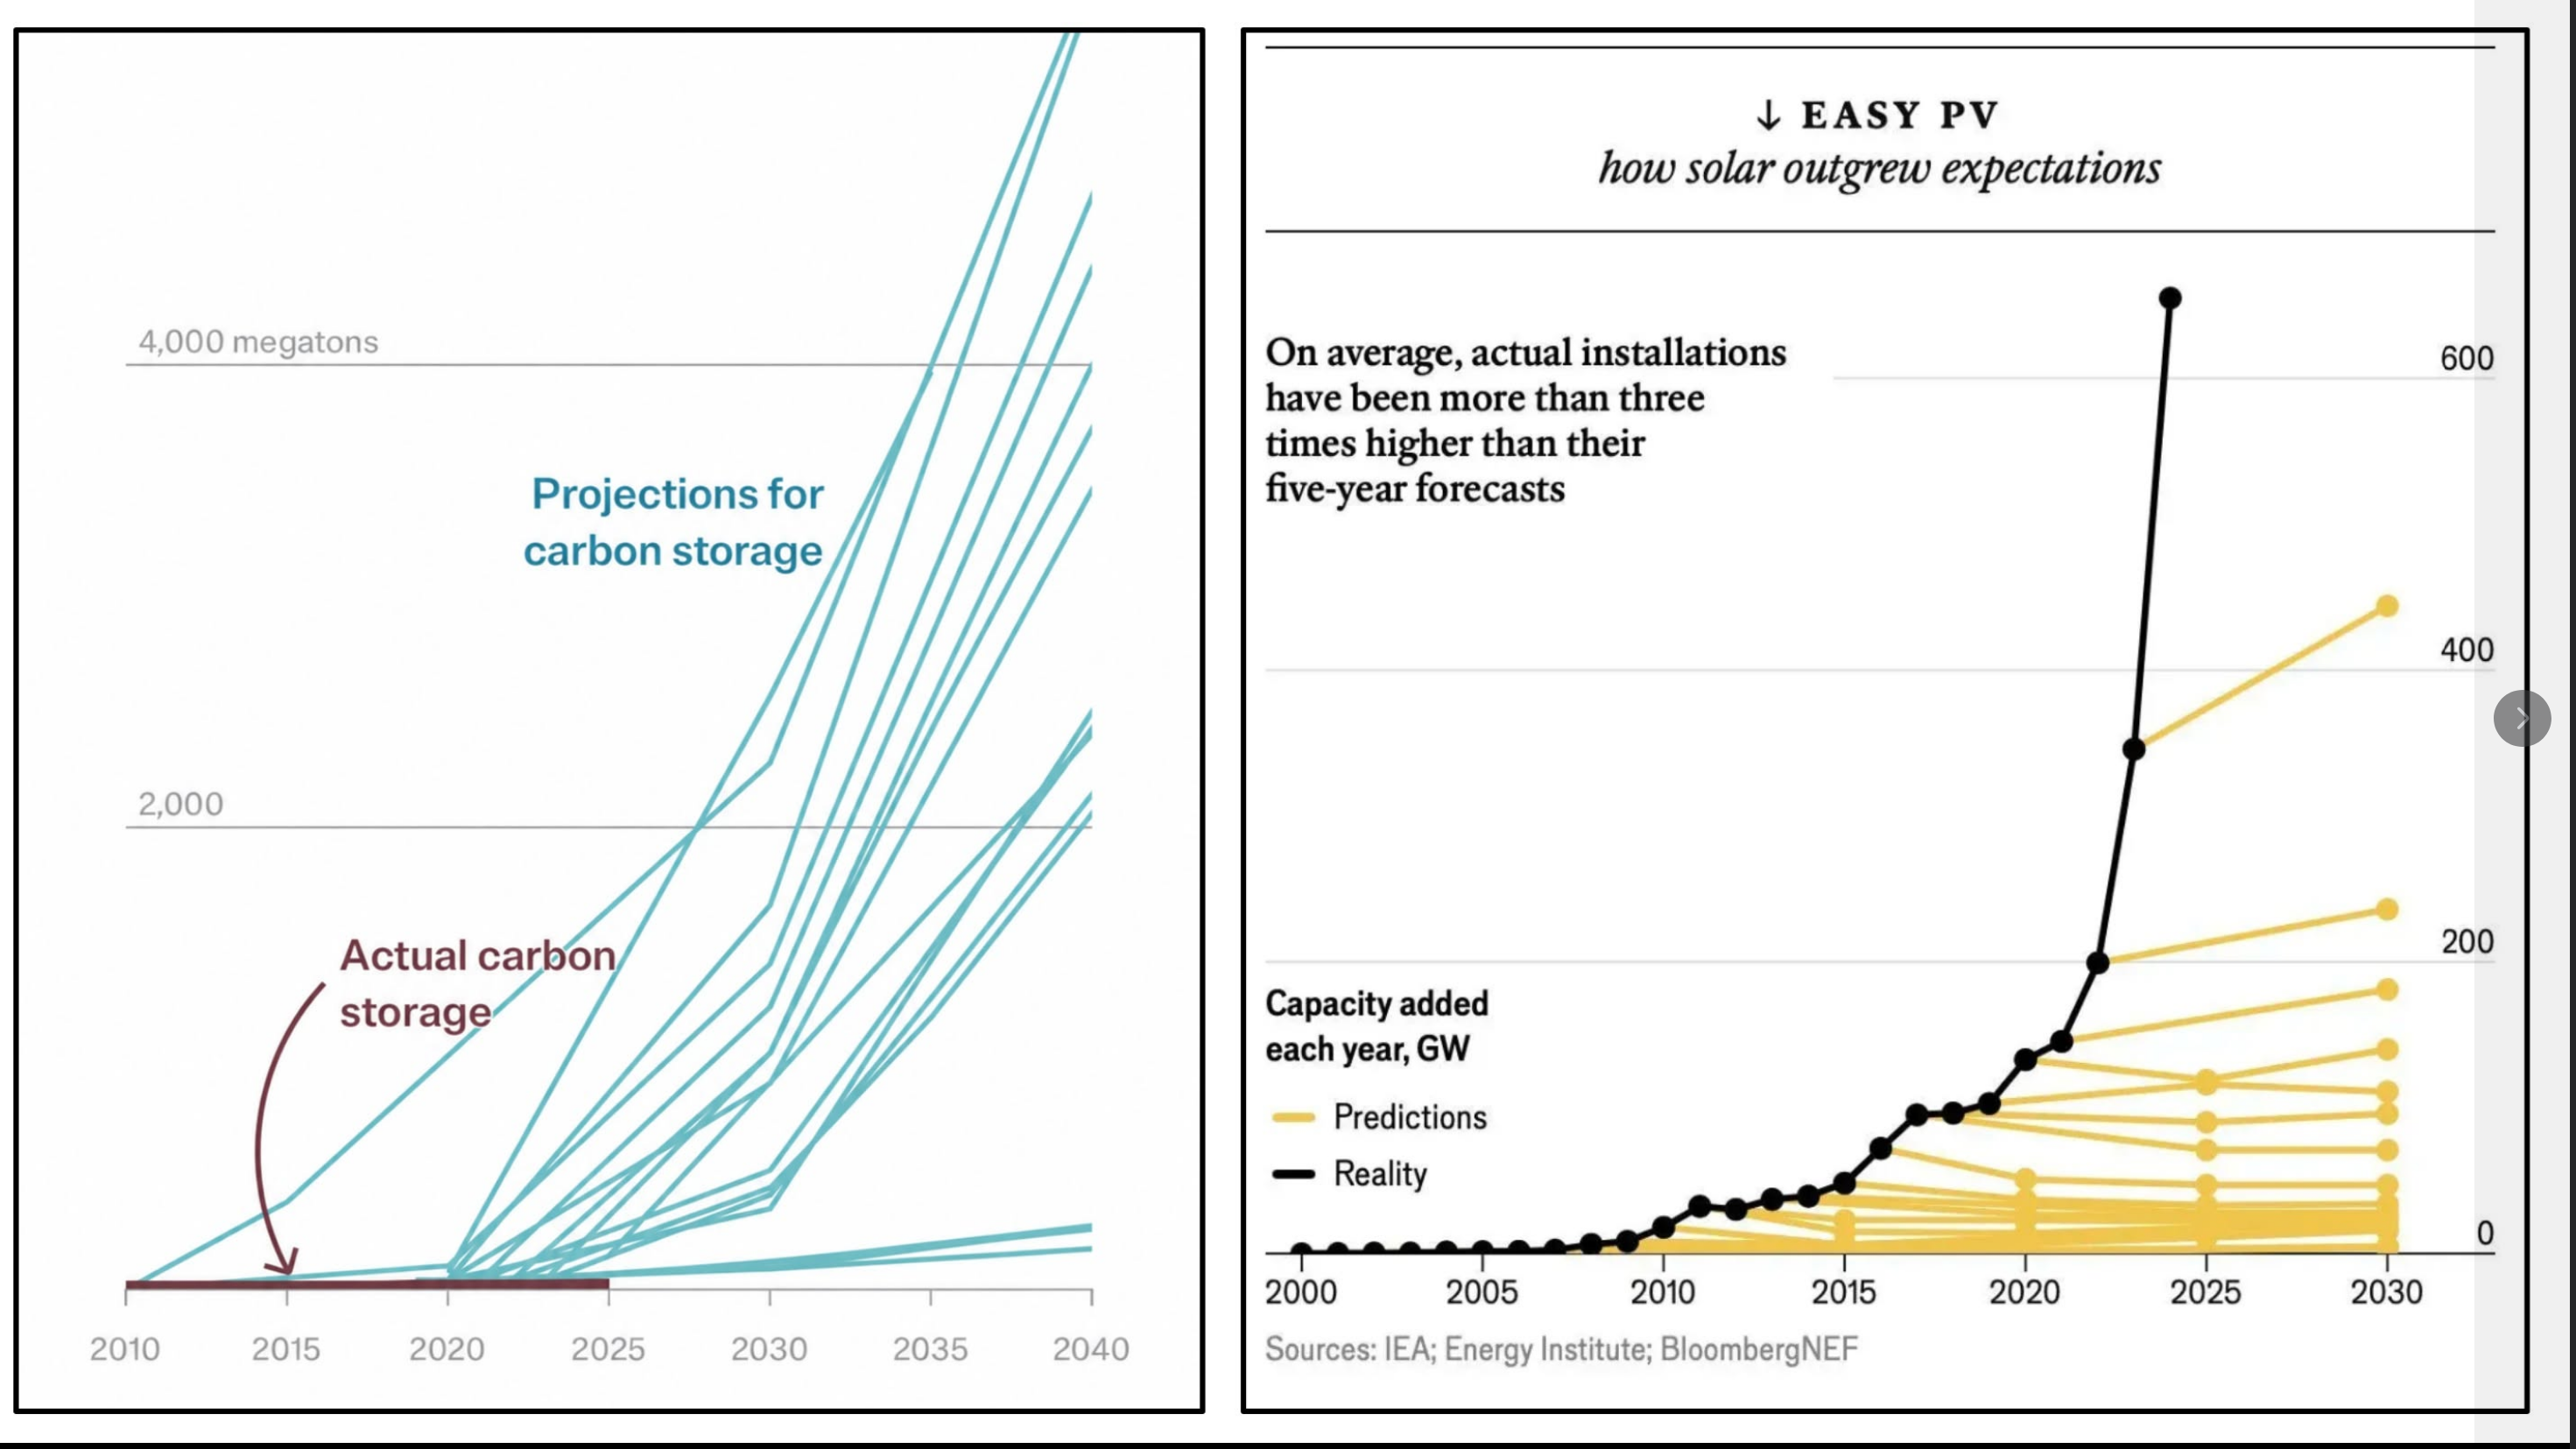
"Carbon capture" is clearly nonsense. Solar is clearly not.

Update on the 9.8 CVSS TCP/IP RCE in the Linux kernel (CVE-2026-98432): we've detected what appears to be a threat actor activity scanning the entire internet for exposed affected systems. Our own scanning also suggests that the number of potential targets is high, therefore there is an increased likelihood of threat actors attempting to develop exploits for the vulnerability.
while CVE-2026-98432 is believed to require MPTCP to be enabled in the kernel, as well as a listening app/service which binds an MPTCP socket, which many have suggested should be rare, several kernels including Debian enable MPTCP by default.
Additionally, Go 1.24+ binds MPTCP sockets by default if the option is enabled in the kernel, so anything built on top of Go (including Caddy) will create the required MPTCP listener.
The mitigation of setting net.mptcp.enabled=0 disabled MPTCP, but does not apply to existing sockets, so any applications that have bound MPTCP sockets need to be restarted, otherwise the system remains exploitable.
You can check if your server is running any MPTCP listeners with the following command: sudo ss -Mlnp
On 2026-10-30 our preliminary internet-wide scan of port 443 confirmed that there are approximately 2,102,043 servers that are successfully reachable via an MPTCP connection. A deeper scan which attempts to connect to each endpoint on port 443 and negotiate a full TLS connection with MPTCP enabled returned about 762,774 systems.
Neither scan can confirm that these are unpatched kernels, just total exposure, but it's a lot more systems than expected. Since a valid HTTP connection is not required to exploit the vulnerability, the total attack surface is likely closer to the 2.1 million number than the 763k one.
As of today (2026-11-02), we've picked up several residential proxies and VPNs scanning the internet on port 443 using MPTCP-enabled connections. Since regular scanners do not negotiate MPTCP by default, and no data is being sent to the HTTP server over 443, we strongly suspect this activity is scanning for CVE-2026-98432 specifically. The use of residential proxies and RU-based VPN servers suggests that this is likely threat actor scanning, rather than security researchers.
Currently there are no known publicly available remote code execution exploits, but there are several denial of service proof-of-concepts floating around. This code gives threat actors a starting point to begin attempting to weaponize the vulnerability. Building exploits for the vulnerability is reported to be extremely difficult, but several state-sponsored threat actors likely have the resources required to succeed.

Advice to children in the 1980s: do not talk to strangers
Advice to children in the 2000s: do not talk to strangers on the computer
Advice to children now: DO NOT TALK TO THE COMPUTER